
GitHub has made cache-mode generally available, bringing least-privilege controls to the GitHub Actions cache. Teams can allow reading, writing, write-only access or disable the cache entirely at workflow or job level.
Quick answer
| Mode | Effect |
|---|---|
read | Restores caches but cannot save changes. |
write | Allows both restores and saves. |
write-only | Saves a cache without restoring one. |
none | Blocks all cache access. |
Why a cache is a security boundary
Caches speed up dependency installation and builds, but they also move files between runs. If a low-trust workflow can write to a key later consumed by a privileged release job, it may try to plant a malicious artifact. A performance feature can therefore become a supply-chain path.
GitHub keeps conservative defaults. Low-trust events such as pull_request_target receive read access, while trusted events such as push retain read and write. Existing workflows keep those secure defaults unless they opt into an explicit mode.
Fine-grained and inherited restrictions
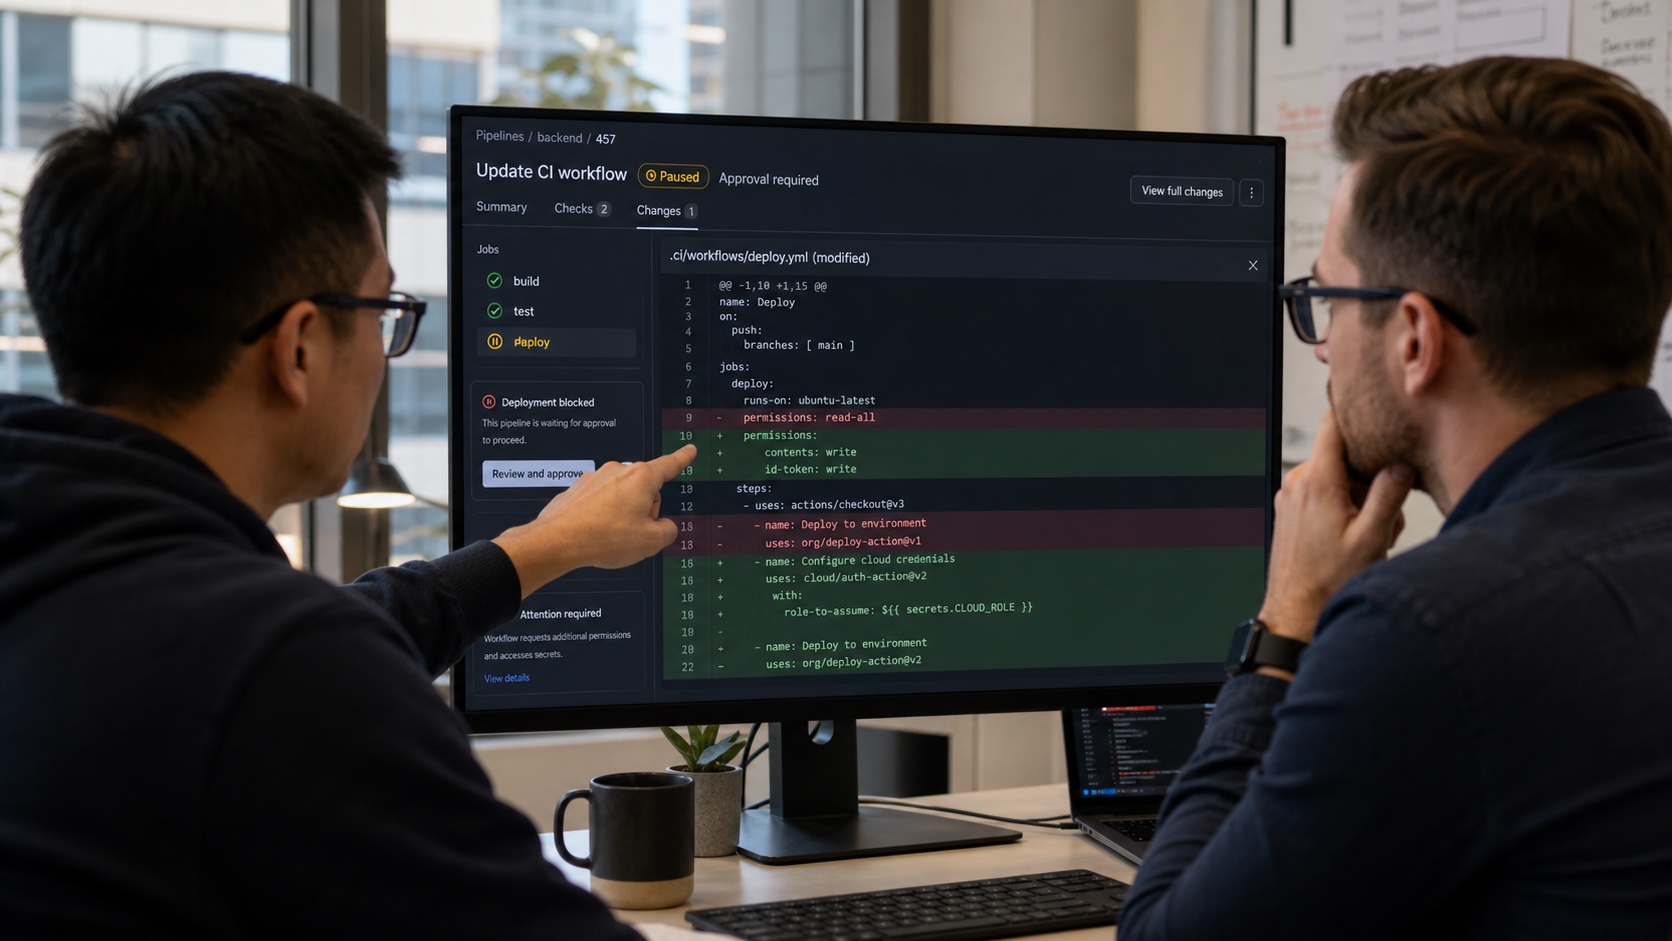
A job-level value overrides the workflow setting. Reusable workflows cannot gain more cache access than their caller granted, preventing a shared component from quietly restoring write permissions in a restricted context.
GitHub also adds a warning annotation when a workflow explicitly grants write or write-only to a low-trust event. The warning is not a substitute for review, but it makes a dangerous exception visible.
A practical migration
First identify which jobs truly restore or save caches. Pull-request tests commonly need only read; a build on the default branch may keep write. Publishing jobs that do not rely on cached state can use none.
Then monitor duration and cache misses. write-only is useful for a dedicated job that produces a clean cache without trusting previous state, but it should remain an intentional, documented choice.
What teams should take away
cache-mode does not fix a compromised action or replace dependency pinning and secret isolation. It does close an important implicit permission. Because it is available on every GitHub plan, CI owners can now clearly separate workflows that consume cached artifacts from those allowed to publish them.
Join the discussion
Comments
Loading comments…