
Cloudflare has opened early access to Managed Defense, a service that finds vulnerabilities in authorized applications, validates exploitability and proposes a patch or WAF rule. It uses OpenAI Daybreak, including GPT-5.6 Cyber.
Quick answer
| Stage | Function |
|---|---|
| Discovery | Code analysis and reconnaissance. |
| Validation | Controlled attempt to confirm the weakness. |
| Remediation | Proposed patch and, when useful, WAF rule. |
| Decision | Human review before application. |
Prioritizing real flaws
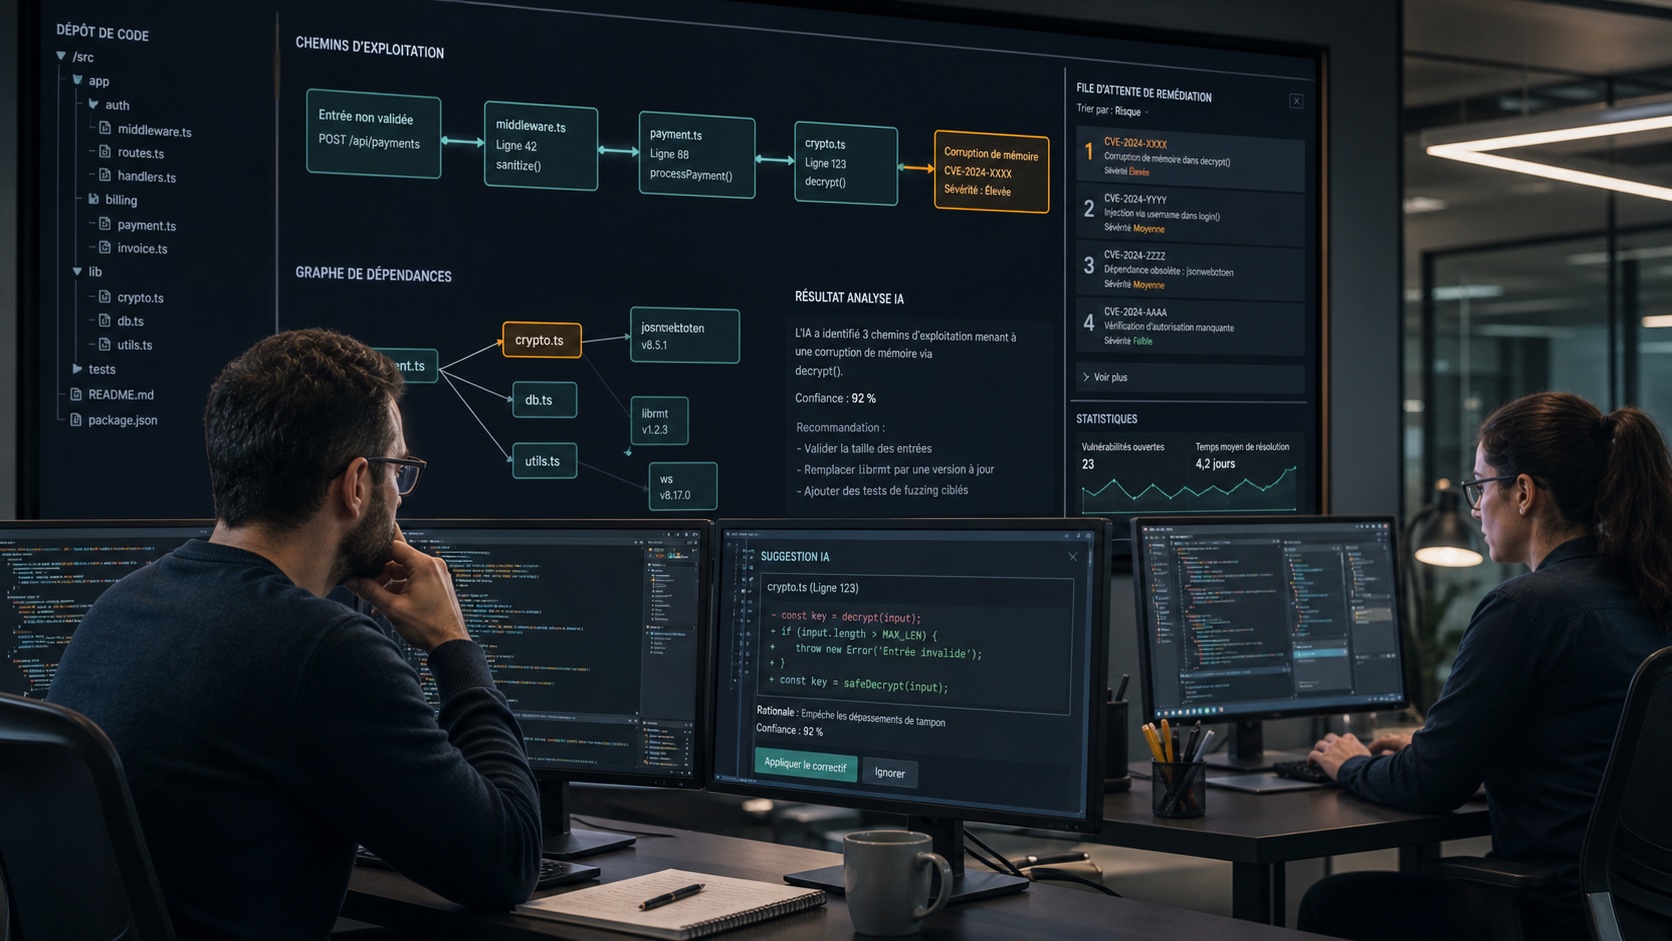
Scanners generate many theoretical signals. Managed Defense tries to connect a weakness to a reachable path. Reproducible evidence helps prioritize real risk, but requires sharing sensitive repository and application context.
AI proposes, humans deploy
Cloudflare says changes are not applied autonomously. The service prepares a fix and possibly a temporary WAF mitigation. Tool calls are logged and models run on OpenAI through AI Gateway. Tests and gradual deployment remain mandatory.
Scoping a pilot
Define permitted repositories, domains and environments. Review retention and log access, then measure true positives, time saved and regressions. A raw vulnerability count is not enough.
More continuous defense
The service brings offensive research closer to remediation, stages often separated by days. In early access it remains a supervised assistant, not a replacement for code review, penetration testing or the team accountable for accepting a patch.
Join the discussion
Comments
Loading comments…