
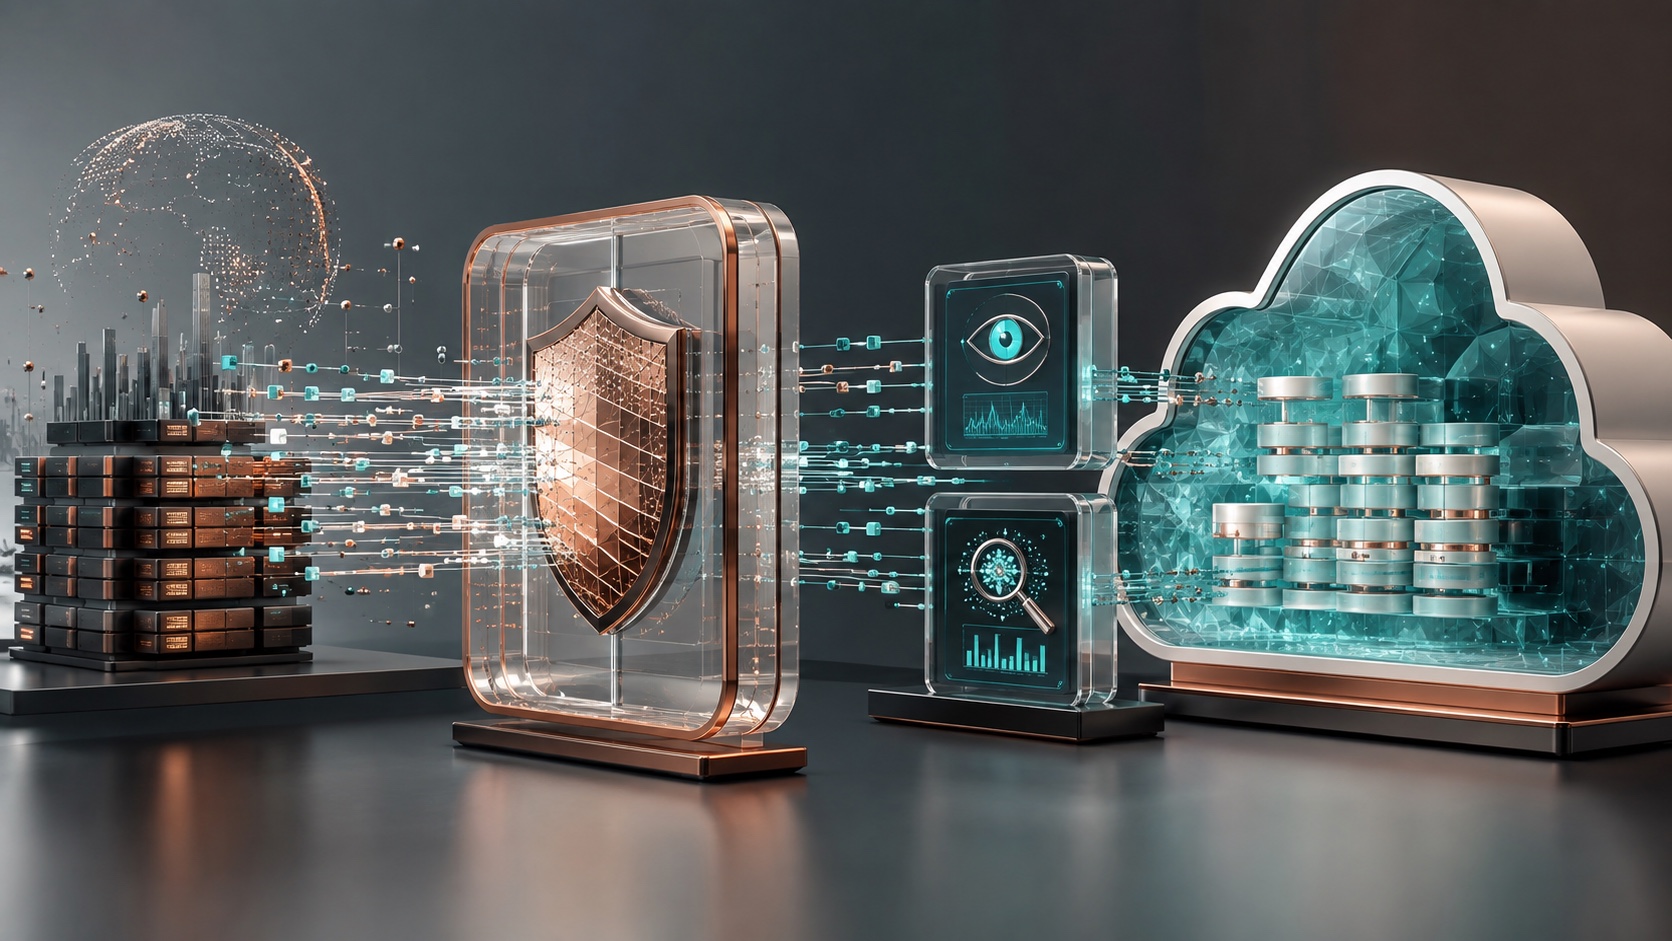
Anthropic has introduced Enterprise Frontier Safeguards, an offering intended to reconcile two difficult requirements: avoiding provider-side retention of an organization's prompts while still detecting uses that could cause serious harm. Rollout is planned for later this fall.
The short answer
| Component | Stated promise |
|---|---|
| Zero Data Retention | Inputs and outputs are not retained by Anthropic after processing. |
| Misuse detection | Signals identify potentially high-risk behavior. |
| Customer storage | Control data is stored in cloud infrastructure controlled by the organization. |
Anthropic says it developed the system with more than one hundred customers. It is intended to support Claude Code, Claude Enterprise, the API platform and offerings delivered through AWS, Google Cloud and Microsoft.
Privacy versus monitoring
A zero-retention policy protects secrets sent to a model, but normally reduces the evidence available after an incident. Logging every conversation creates a different sensitive database. The proposed approach moves part of the audit trail into customer infrastructure, where the organization controls access and retention.
That does not remove architecture questions. Customers need to know which events are copied, in what form, with which encryption keys and which identities can read them.
A product cannot replace internal policy
Misuse detection targets severe scenarios, but without business context it cannot always distinguish legitimate research from attempted exfiltration. Alerts must connect to identities, permissions and incident procedures without becoming indiscriminate employee surveillance.
Legal, security and workforce teams should define purpose, proportionality and log retention. In Europe, a security feature still has to respect minimization and transparency principles.
Checks before adoption
Ask for the signal catalog, expected false-positive rates, supported regions and contractual guarantees. Test what happens when customer storage is unavailable: does the application continue, block requests or merely lose visibility?
A proof of concept should include harmless activity resembling abuse, genuinely prohibited requests and an investigation exercise. Time from event to alert matters as much as raw detection rate.
A new responsibility boundary
In this model, the provider analyzes risk while the customer holds the control records. That separation may improve confidentiality, but it transfers operational duties: bucket security, key rotation, analyst access and deletion.
Enterprise Frontier Safeguards addresses a real tension in enterprise AI deployments. Its value will depend less on the “zero retention” label than on transparent event semantics and customers' ability to operate those signals without creating another data risk.
Join the discussion
Comments
Loading comments…