
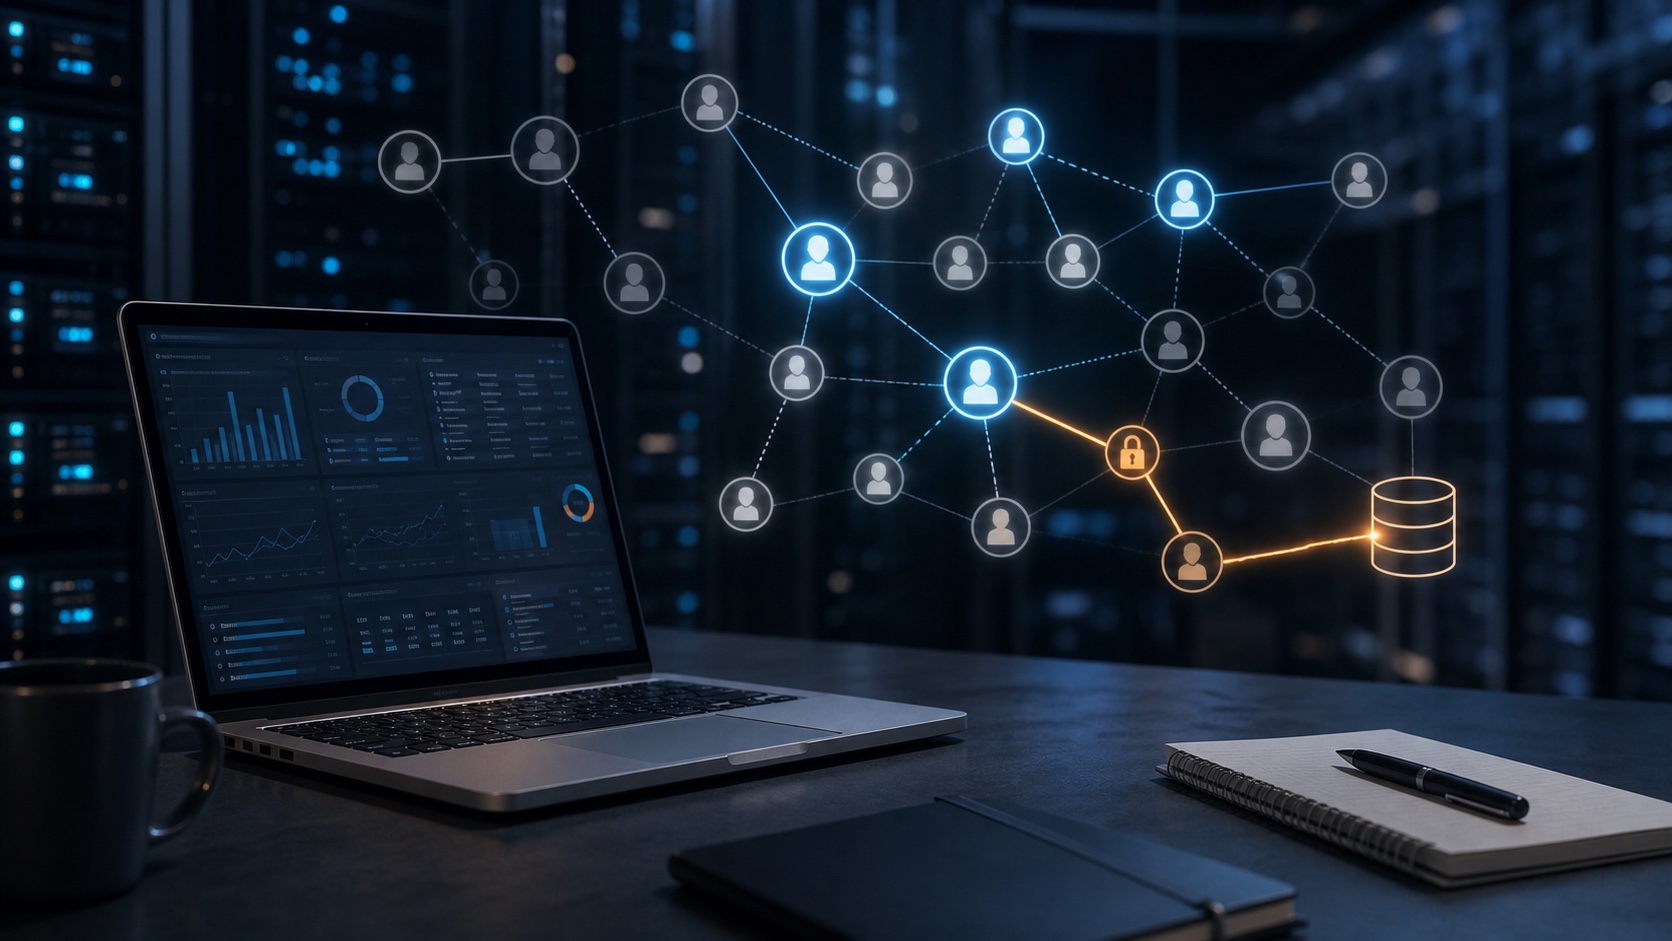
In cloud environments, identity is often the real perimeter. Machines, serverless functions, managed services and humans access resources through roles and keys.
Over time, projects change, teams move and integrations remain. Rarely used accounts then keep privileges that are too broad.
What Is Changing
For attackers, a dormant identity is ideal: it triggers few alerts and can provide access to data or expensive compute capacity.
This subject is useful because it sits at the intersection of technical choices, product expectations and operational reality. The teams that make progress are rarely the ones that chase every trend. They are the ones that translate the signal into a smaller set of decisions: what to build, what to measure, what to document and what to stop.
Why It Matters
Review inactive access, reduce rights, enforce short lifetimes, monitor keys and integrate IAM into sprint or operations reviews.
In a daily workflow, the difference often comes from preparation. A clear owner, a short checklist, a measurable target and a rollback path turn a promising idea into something that can be operated. Without those elements, even a good technical choice becomes fragile.
What To Watch
The trap is believing IAM was solved at launch. Permissions drift, exceptions become permanent and local keys leave vaults.
The other weak point is communication. Users, buyers and internal teams do not need every implementation detail, but they need to understand what changed, what remains uncertain and where responsibility sits. That clarity prevents confusion when the system behaves differently from a classic tool.
A Pragmatic Method
The practical starting point is modest: choose one use case, define the expected result, measure the current baseline and introduce the new approach behind a controlled path. Then compare quality, cost, support load and user confidence before expanding.
For teams publishing or operating digital products, this also means keeping artifacts close to the product itself: release notes, help text, dashboards, test cases and incident notes. The more these elements live in separate documents, the harder they are to maintain.
Our Read
Cloud security does not start with the firewall. It starts with knowing who can do what, and since when.
Join the discussion
Comments
Loading comments…