
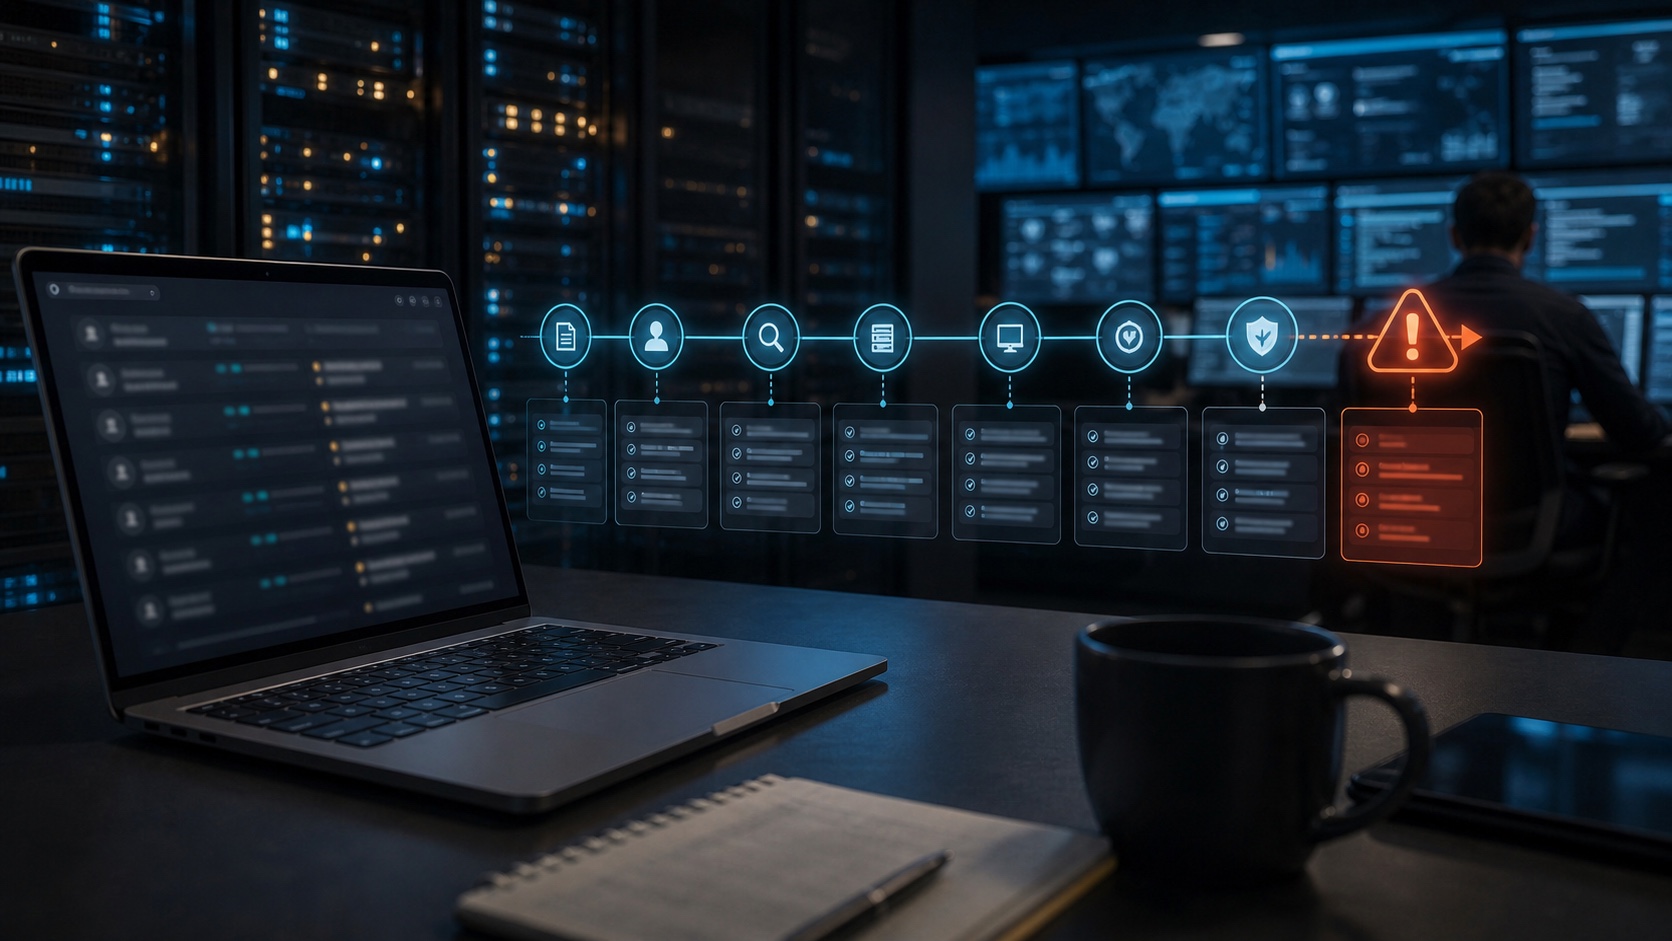
During an incident, the first question comes quickly: what happened? Without reliable logs, the answer becomes slow, expensive and sometimes impossible.
Logs should cover authentication, permission changes, administrative actions, sensitive data access, application errors and important service calls.
What Is Changing
For a small team, a few well-chosen logs are better than an ocean of unreadable events. The goal is to reconstruct a timeline, not store everything without method.
This subject is useful because it sits at the intersection of technical choices, product expectations and operational reality. The teams that make progress are rarely the ones that chase every trend. They are the ones that translate the signal into a smaller set of decisions: what to build, what to measure, what to document and what to stop.
Why It Matters
Define critical events, synchronize clocks, protect log integrity, set retention periods and test a mock investigation.
In a daily workflow, the difference often comes from preparation. A clear owner, a short checklist, a measurable target and a rollback path turn a promising idea into something that can be operated. Without those elements, even a good technical choice becomes fragile.
What To Watch
The risk is twofold: not logging enough to investigate, or logging too much sensitive data and creating a new privacy issue.
The other weak point is communication. Users, buyers and internal teams do not need every implementation detail, but they need to understand what changed, what remains uncertain and where responsibility sits. That clarity prevents confusion when the system behaves differently from a classic tool.
A Pragmatic Method
The practical starting point is modest: choose one use case, define the expected result, measure the current baseline and introduce the new approach behind a controlled path. Then compare quality, cost, support load and user confidence before expanding.
For teams publishing or operating digital products, this also means keeping artifacts close to the product itself: release notes, help text, dashboards, test cases and incident notes. The more these elements live in separate documents, the harder they are to maintain.
Our Read
A good log is both a product and security decision. It should tell the important action without unnecessarily exposing people.
Join the discussion
Comments
Loading comments…