
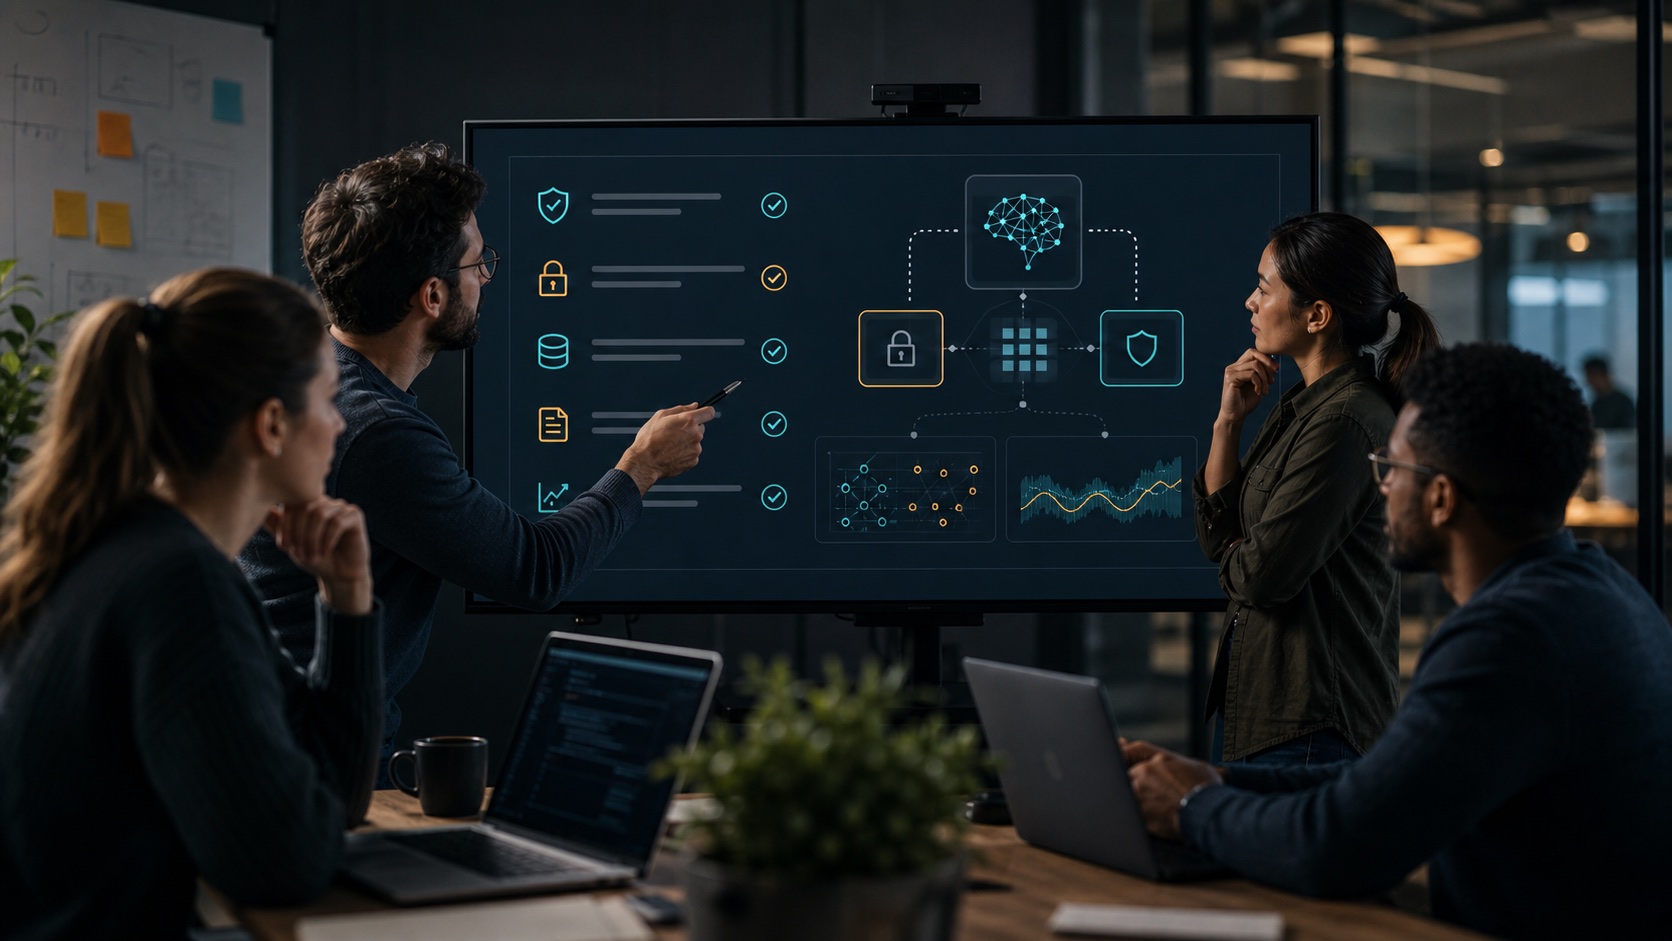
Adding an AI model to a product can look like a normal API integration: input, response, cost to monitor. That reading is too narrow. A model receives context, influences decisions, may produce dangerous instructions and is often embedded in flows where the user does not see every intermediate step.
Security needs to arrive before the public demo, not after it. The goal is not to block AI use cases. It is to prevent a convincing prototype from becoming a data leak, an uncontrolled execution path or a dependency that cannot be audited.
Start with the data map
The first question is simple: what data goes to the model? Teams need to separate public data, internal documents, personal information, technical secrets, contractual data and data covered by regulatory obligations. Not everything belongs in a prompt, even if the model gives a good answer during a demo.
A practical approach is to define data classes and attach usage rules to each one. Some information can be used as is, some must be masked, summarized, pseudonymized or excluded. That decision should be visible in the architecture, not hidden inside a prompt instruction.
Treat outputs as untrusted content
An AI answer can be convincing and wrong. It can also contain a risky command, weak legal guidance, a hallucinated source or sensitive information accidentally pulled from context. That is why output should not be executed, published or sent to a third party without a control matching the risk.
For an internal assistant, human review may be enough. For a tool that modifies data, sends a customer message or triggers a system action, stricter controls are needed: allowlists, thresholds, previews, logging, explicit confirmation and blocking of irreversible operations.
Control connected tools
Risk increases sharply when the model can call tools. A connector to a document store does not have the same impact as a connector to a CRM, cloud drive, Git repository or admin console. Each tool should follow least privilege: reduced access, separated permissions, short scopes and no unnecessary secrets.
Prompt injection often attacks that boundary. A malicious document can try to persuade the model to ignore instructions or leak data. Controls must therefore be technical: separation between system instructions and untrusted content, output filtering, tool-call validation and anomaly detection.
Keep an audit trail
When something goes wrong, the team needs to reconstruct the chain: model version, prompt, parameters, documents retrieved, tool called, decision made, affected user and generated output. Without that trace, it is hard to fix the issue or explain the incident.
That does not mean retaining every bit of data forever. Logging should be proportionate and compatible with privacy rules. But it needs to be sufficient to diagnose incidents, compare model versions and verify that guardrails are working.
Add the right friction
A secure AI integration does not have to be heavy. Simple controls can be automated: secret masking, file-type rejection, schema validation, cost limits, evaluation tests and alerts on sensitive actions. Human validation should be reserved for decisions that affect the company or the user.
The real compromise is making risk visible. A team can accept low friction when an assistant summarizes a public document. It should not accept an agent modifying an invoice, deleting data or running a system command without evidence and authorization.
AI brings speed. Security gives that speed a usable production shape.
Join the discussion
Comments
Loading comments…